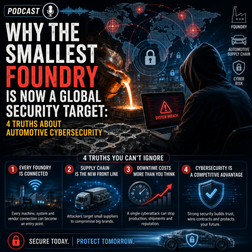
Why the Smallest Foundry is Now a Global Security Target: 4 Truths About Automotive Cybersecurity
You can use my code F40 for discount of products that you can find on my deals page on following link:https://mydeals.page/1jug Strategic Imperative: Cybersecurity as a Supply Chain Pillar In our current industrial landscape, cybersecurity has evolved from a peripheral IT concern into a core strategic competence for the automotive supply chain. As Chief Cybersecurity Architects, we must recognize that the air gap in modern die casting is a myth. Our foundries are no longer isolated industrial sites; they are high-consequence nodes in a converged IT/OT environment where lateral movement is the primary threat vector. Because die casting foundries produce critical structural, chassis, and drivetrain components in tightly synchronized series, a single failure in our environment does not stay local. It triggers a systemic halt that cascades through machining and assembly to Tier 1 suppliers and, ultimately, OEM production lines globally. The Economic Risk Landscape The financial stakes of a breach are catastrophic and immediate. Data from the Center of Automotive Management (CAM) and VicOne underscores a landscape of aggressive targeting: Daily Production Loss: According to Professor Stefan Bratzel, production downtime results in damages in the double-digit millions per day. Shift in Target Profile: In 2024, 56.9% of all cyberattacks in the automotive sector targeted suppliers rather than OEMs, identifying us as the high-leverage entry point. Systemic Relevance: Foundries are now classified as systemically relevant targets for global cyber actors, where the disruption of a single supplier can paralyze the entire value chain. Evolution of the Supplier Role The digital transformation of our value creation networks has fundamentally changed the supplier's role. We now possess direct, live access to development, production, and quality data. This integration makes us the preferred entry point for sophisticated actors. Because suppliers are historically less robustly protected than major OEMs, we represent a path of least resistance for attackers seeking to compromise the broader ecosystem. This strategic vulnerability necessitates a precise audit of the technical vulnerabilities inherent in the die casting process.