
Notas del episodio
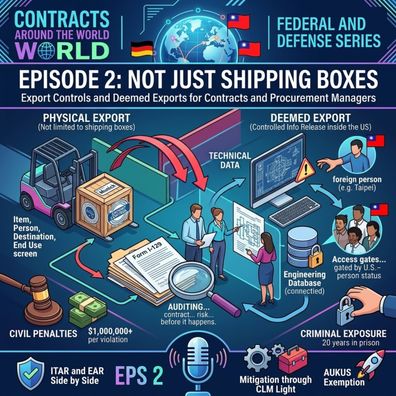
This episode breaks down how everyday procurement actions—such as emailing a CAD drawing or onboarding a non-U.S. worker—can trigger severe U.S. export control violations with multi-million dollar penalties. Operating as expert procurement and contracts guides, the hosts debunk the "shipping box myth" by detailing the mechanics of deemed exports, comparing the zero-tolerance ITAR "see-through" rule against the EAR de minimis threshold, highlighting hidden gaps in HR, IT, and cloud environments, and laying out an actionable 30-60-90 day compliance playbook.
Podcast Episode Notes
1. The "Shipping Box Myth" & High-Stakes Penalties
- The 90-Second Violation
- Severe Liability
- Real-World Enforcement Case Studies
2. Deemed Exports & Defining a "Foreign Person"
- The Clean Room Analogy
- Legal Definition
- Everyday Leaks
3. Regulatory Frameworks: ITAR vs. EAR
- ITAR (State Dept / DDTC)
- EAR (Commerce Dept / BIS)
4. Order of Review & Evaluation Mechanics
- Mandatory Order of Review
- The "Specially Designed" Trap
- The 4-Question Screen
- The Encryption Trap
5. Internal Leaks: HR, IT, & Cloud Security
- Passport Divergence
- Form I-129 HR Gap
- The Cloud & FedRAMP Illusion
- Defense Services Felony
6. Operating Models & Global Supplier Friction
- 3 Operating Models:
- Enclave & Data Minimization (Safest)
- License & Share (Brittle)
- Design Out (Hardest)
- The "ITAR Free" Myth
- GDPR Workarounds
- Chief Compliance Officer legal attestation and enforcing role-based access controls rather than collecting employee passport copies.
7. Case Studies, Rules, & Emergency Protocols
- Professor John Reece Roth Case
- The Affiliates Rule
- 24-Hour Emergency Protocol:
8. The 30-60-90 Day Action Plan